Experience Fast Quick Cloud Servers
A Virtual Private Cloud (VPC) is a private cloud computing environment hosted within a public cloud. Essentially, a VPC creates logically isolated sections of the public cloud to provide a virtual private environment.
Like all cloud environments, VPC resources are available on-demand, allowing for scalable and highly configurable solutions.
VPC from Quicservers allows you to define a private network using a mix of cloud and bare metal servers, tailored to suit your multi-tier application and network environments. You can launch your databases in a private subnet while keeping your user-facing application servers or firewall in the public subnet.
With Quicservers VPC, you gain all the security and tiered architecture benefits that hyperscalers offer, but at a much lower cost.
Contact us for your custom requirements. Our solutions team is ready to answer your queries and assist you in setting up the Virtual Private Cloud.
Enter your Requirement
Overview of Virtual Private Cloud
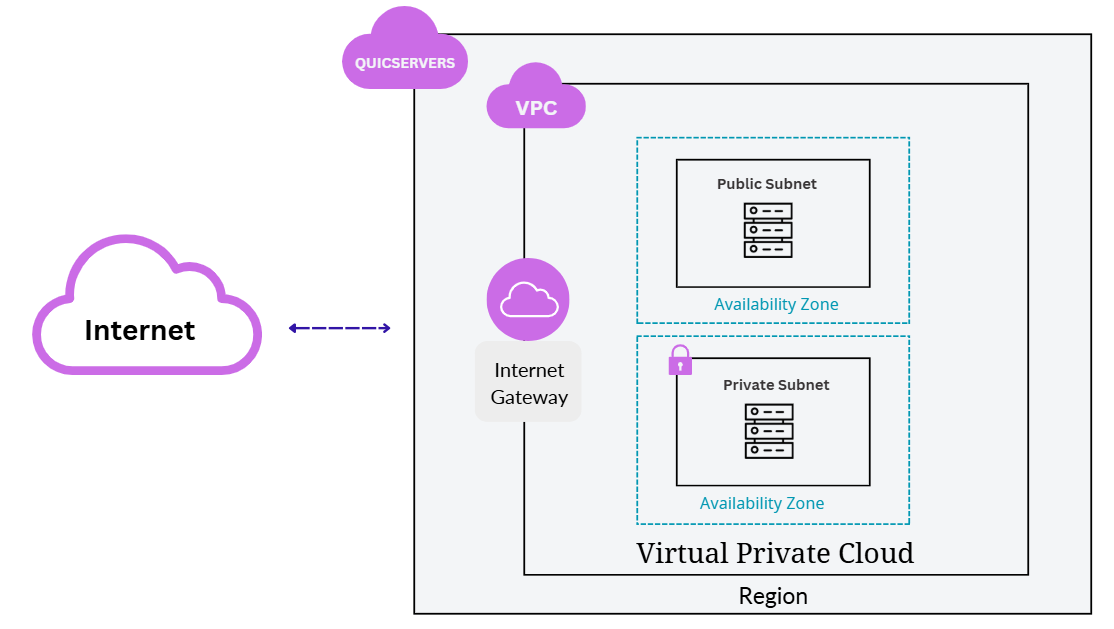
This diagram illustrates the architecture of a Virtual Private Cloud (VPC), which provides an isolated network environment within a cloud provider’s infrastructure. The VPC contains two primary subnets: a public subnet and a private subnet. The public subnet is connected to the internet through an Internet Gateway, making it suitable for hosting resources like web servers that need external access. In contrast, the private subnet is secured and isolated, used for sensitive resources like databases that do not require direct internet access. Both subnets are deployed across Availability Zones within a specific region, ensuring high availability and fault tolerance. The diagram also highlights the “Quicservers” service operating within this environment, emphasizing the secure and organized flow of data. The private subnet is further secured with restricted access, showcasing the importance of safeguarding critical resources. Overall, the architecture ensures scalability, security, and efficient management of cloud resources.
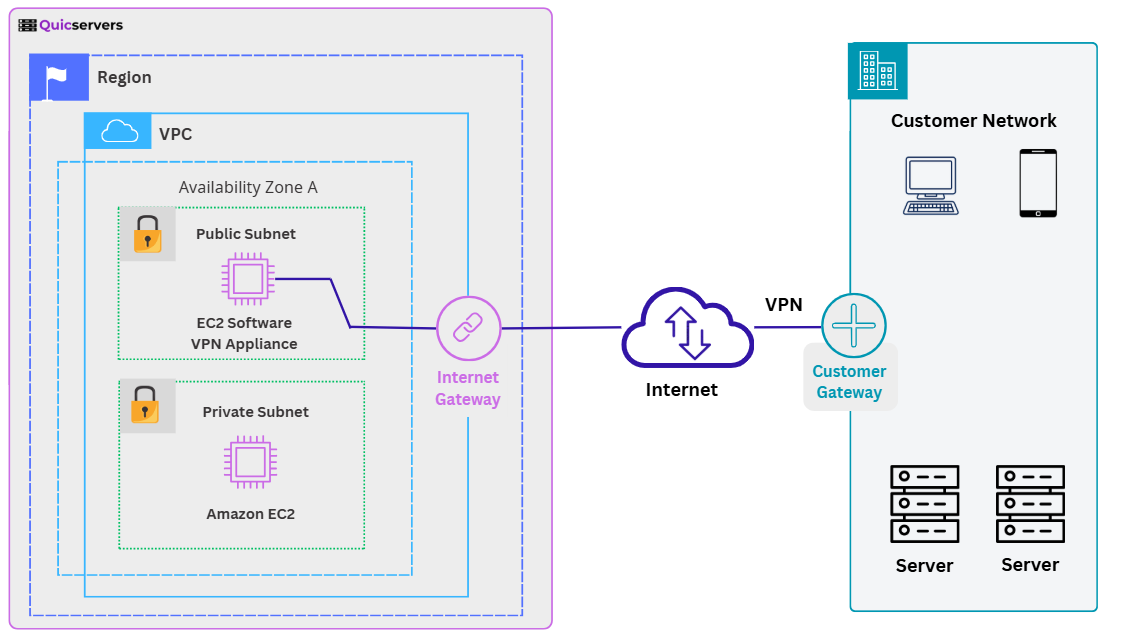
This diagram represents a secure connection between a Virtual Private Cloud (VPC) and a customer network via a Virtual Private Network (VPN). The VPC resides within a specific region and includes a public subnet and a private subnet in Availability Zone A. The public subnet hosts an EC2 Software VPN Appliance, which facilitates secure communication between the VPC and the customer network. The private subnet houses an Amazon EC2 instance for running internal applications or services.
An Internet Gateway connects the VPC to the internet, allowing the VPN Appliance to establish a VPN connection. The customer network, located on-premises or elsewhere, connects through a Customer Gateway, ensuring secure access to VPC resources. This setup provides an encrypted communication channel, safeguarding data transfers over the internet while enabling seamless integration between cloud and on-premises resources. It also highlights a secure architecture for remote access and hybrid cloud environments.
Need some assistance? We're always here for you
Our Support team is fully prepared to address all your concerns and deliver the technical assistance you need to ensure your server’s success.
Enter your details
